How to Hide API Keys When Recording with QuickTime Player
You press Cmd+Shift+5 to quickly record your screen for a bug report, a Slack demo, or a pull request walkthrough. Five minutes later, you realize the recording captured your open .env file with production credentials. Here is how to make that impossible.
QuickTime: The Recording Tool You Use Without Thinking
QuickTime Player is built into every Mac. There is nothing to install, nothing to configure. Press Cmd+Shift+5 and you are recording your entire screen or a selected portion within seconds. This makes it the default choice for quick, informal recordings -- the kind developers make dozens of times per month.
That convenience is exactly the problem. When you fire up OBS or ScreenFlow, there is a mental "I am recording now" moment. You check your screen, close sensitive files, prepare. But QuickTime recordings happen on impulse. A colleague asks "can you show me that bug?" and you hit the keyboard shortcut before thinking about what is on screen.
Common QuickTime Recording Scenarios for Developers
- Bug reports -- Recording steps to reproduce an issue for a GitHub issue or Jira ticket
- Async code reviews -- Walking through a PR with screen recording instead of a live call
- Quick demos -- Showing a feature to your PM or design team via Slack
- Documentation -- Recording setup steps for internal onboarding wikis
- Interview prep -- Recording yourself solving coding problems for review
In every one of these scenarios, your editor is front and center -- and so are any secrets in your open files.
Why QuickTime Recordings Are Especially Risky
QuickTime screen recordings tend to be shared more casually than polished tutorial videos. You record, save the .mov file, and drag it directly into Slack, a GitHub comment, or a Google Doc. There is no editing step where you might catch an exposed secret. The raw recording goes straight to your audience.
Even recordings meant for internal use can become a risk. Slack messages get searched. Google Docs get shared with new team members. Internal wiki pages become accessible to contractors. A "quick recording for the team" today might be visible to a much wider audience six months from now.
STRIPE_SECRET_KEY=sk_live_51H7bG2CjPn...
DATABASE_URL=postgresql://admin:S3cretP@ss@db.internal:5432/prod
GITHUB_TOKEN=ghp_xK9mN2pL4qR8vZwYtU...
JWT_SECRET=a7f2c9e1d4b8...
Manual Workarounds (and Their Limits)
1. Check Your Screen Before Recording
The advice sounds simple: look at what is on screen before you press record. But QuickTime's Cmd+Shift+5 flow is designed to be fast. By the time you see the recording toolbar, you are already thinking about what you want to demonstrate, not about which files are open in your editor three spaces away.
2. Use Selection Recording Instead of Full Screen
QuickTime lets you record a selected portion of your screen. You could drag a selection that excludes your .env tab. But this is fragile -- you might scroll, switch tabs, or resize a window, bringing secrets into the captured area.
3. Edit the .mov File After Recording
QuickTime has basic trim functionality, but no blur or redaction tools. To add blur, you need to import the recording into iMovie, Final Cut Pro, or another editor. For a "quick recording" that was supposed to take 30 seconds, this adds 10-15 minutes of work -- and you probably will not bother.
The Automated Solution: PixelHush + QuickTime
PixelHush is a macOS menu bar app that detects when any screen recording starts -- including QuickTime Player -- and automatically masks secrets in your code editor. QuickTime detection works on the Free tier with zero configuration.
How QuickTime Detection Works
PixelHush watches for the macOS Screenshot toolbar (Cmd+Shift+5) and QuickTime Player. As soon as either one opens, PixelHush treats it as a recording and masks secrets in your editor -- before you click "Record." Close it, and your secrets come back.
PixelHush then signals its editor extension (VS Code, Cursor, Windsurf, or Antigravity) to activate masking. Protected config files in your editor switch to a protected view with every value masked. The actual file content is never changed -- only what you see on screen.
QuickTime Player and the macOS Screenshot toolbar (Cmd+Shift+5) use standard system screen capture APIs. PixelHush detects them automatically on the Free tier, alongside macOS Built-in, OBS Studio, Zoom, and Chrome. Loom, ScreenFlow, Screen Studio, CleanShot X, and the other Pro apps require a paid subscription.
STRIPE_SECRET_KEY=••••••••••••••••••••
DATABASE_URL=••••••••••••••••••••
GITHUB_TOKEN=••••••••••••••••••••
JWT_SECRET=••••••••••••••••••••
Setup: PixelHush with QuickTime
- Install PixelHush -- Download from pixelhush.dev and drag to Applications.
- Install the editor extension -- Open VS Code, go to Extensions, search "PixelHush", install. The extension auto-connects to the menu bar app via local WebSocket on port 39271. Supports VS Code, Cursor, Windsurf, and Antigravity.
- Verify connection -- Check the VS Code status bar for the PixelHush item: it reads Off and switches to On while QuickTime records.
- Record with QuickTime -- Press Cmd+Shift+5 or open QuickTime Player and choose File > New Screen Recording. Secrets are masked as soon as the capture toolbar or QuickTime Player opens.
- Stop recording -- Click the stop button in the menu bar or press Cmd+Control+Escape. Secrets unmask when the capture app closes: quit QuickTime Player, or close the Cmd+Shift+5 toolbar.
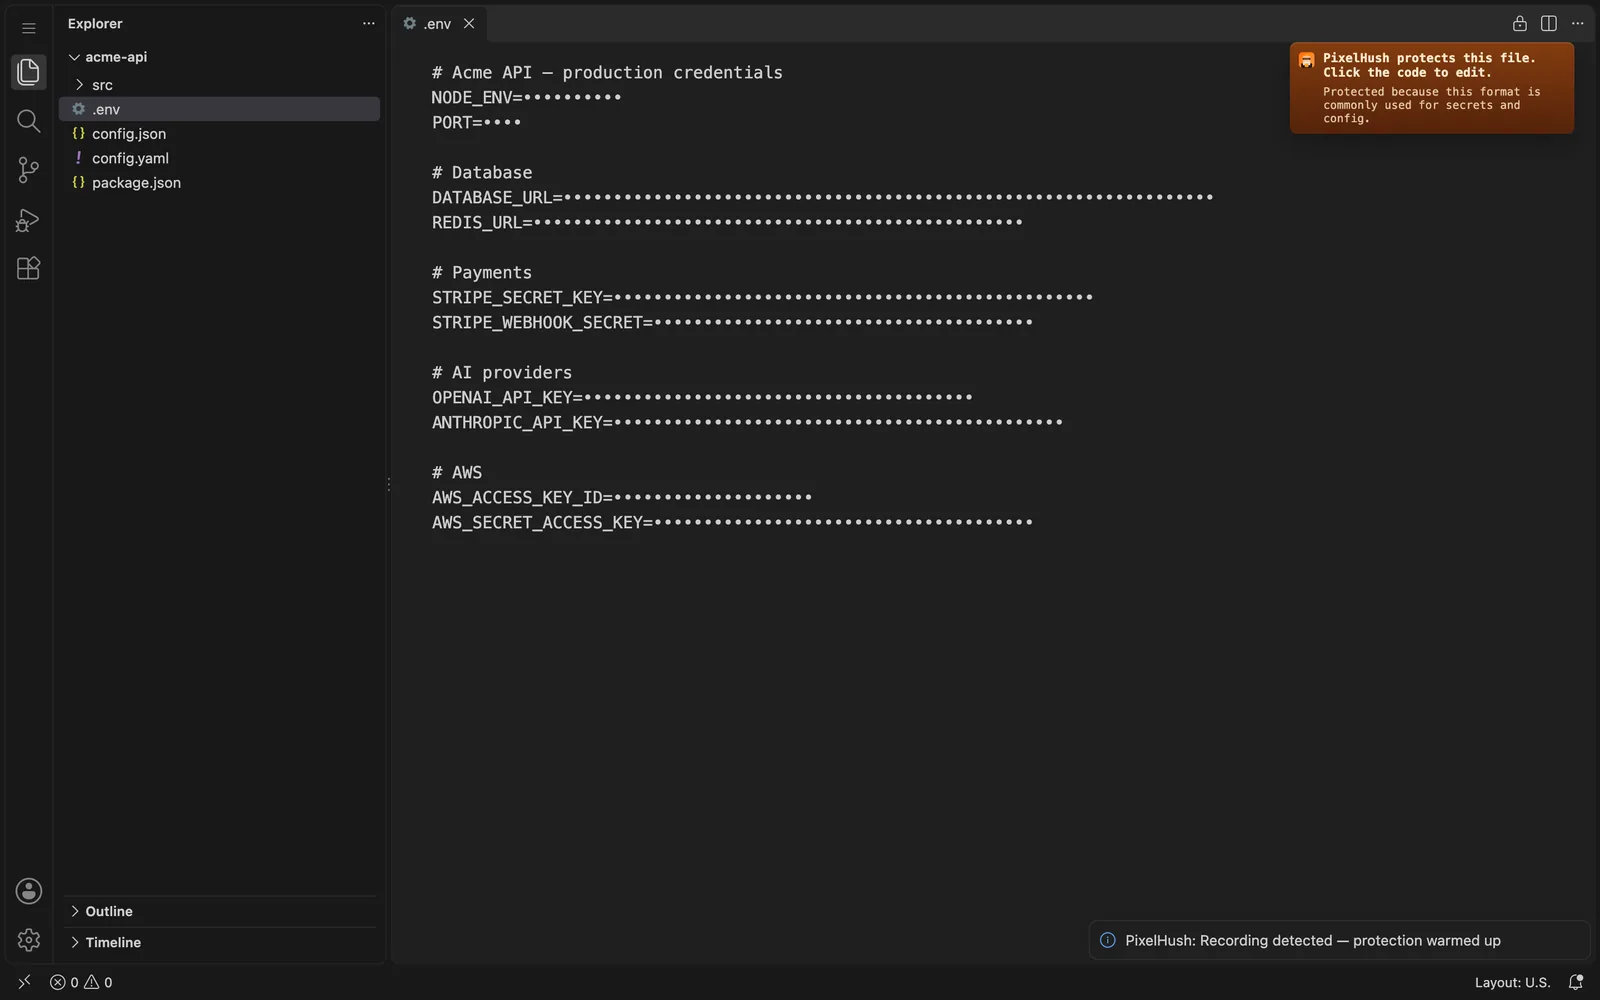
.env is masked.QuickTime-Specific Scenarios
Bug Reports with Screen Recordings
Modern issue trackers like GitHub, Linear, and Jira all support embedded video. Recording a bug with QuickTime and attaching it to a ticket is faster than writing detailed reproduction steps. With PixelHush, you can record freely without worrying that your .env or config files are visible in the background.
Async Code Reviews
Instead of scheduling a 30-minute call to walk through a complex PR, record a 5-minute QuickTime video explaining your changes. Your reviewer watches on their own schedule. PixelHush ensures that any secrets visible in your editor during the walkthrough are automatically masked, even if you switch to a configuration file to explain a change.
Slack Quick Shares
The most dangerous pattern: record screen, drag .mov into Slack, done. No editing step, no review. With PixelHush running, this workflow stays safe. Secrets are masked before the pixels are captured, so the recording file itself never contains visible credentials.
Comparison: QuickTime Recording Safety
| Approach | Time Added | Reliability | Works for Quick Shares |
|---|---|---|---|
| Check screen manually | 30-60 seconds | Easy to forget | Breaks the fast workflow |
| Selection recording | 10-20 seconds | Scroll/resize can expose | Limited view area |
| Edit in iMovie after | 10-15 minutes | Might miss frames | Defeats the purpose |
| PixelHush | Zero | System-level, automatic | Instant, no workflow change |
What Gets Masked
While a recording is detected, PixelHush protects .env files, config-style JSON (config.json, secrets.json, credentials.json, service-account keys), YAML, config TOML and shell scripts. In these files it masks every value by default, so it never has to guess which key is sensitive:
- API keys -- Stripe, OpenAI, AWS, Google Cloud, GitHub, Slack, Twilio, SendGrid
- Database connection strings -- PostgreSQL, MySQL, MongoDB, Redis URIs with credentials
- Authentication tokens -- JWT, OAuth, session keys, bearer tokens
- Infrastructure secrets -- SSH keys, TLS certs, Docker registry credentials
- Everything else in the file -- ports, hostnames and flags are masked too. Prefer to keep them readable? Turn on selective mode (
pixelhush.selective.enabled) and PixelHush masks only keys matching its 58 built-in patterns, such as*_KEY,*SECRET*and*PASSWORD*, plus values that look like tokens
Chrome Extension for Full Coverage
If your QuickTime recording also shows a browser -- AWS Console, Stripe Dashboard, Vercel settings -- the PixelHush Chrome Extension masks secrets in web pages too. Between the editor extension and the Chrome extension, every part of your screen that contains credentials is covered.

Stop leaking secrets. Start recording freely.
Join developers who share code safely every day with PixelHush.